Complass – Navigate compliance Complass – Navigate compliance

Framework

ISO/IEC 27001:2022

Step by step to an information security management system per ISO/IEC 27001:2022, with IT and production in mind.

Still from the short video “Compliance management in 20 seconds”
Compliance management in 20 seconds Project, next step, checklist, Statement of Applicability, audit package. Beispieldaten der Demo-Firma.

What is ISO 27001?

ISO/IEC 27001 is the international standard for information security management systems (ISMS). It specifies how a company plans, implements, monitors and improves information security based on risk; Annex A contains 93 controls whose applicability is justified in the Statement of Applicability.

Content as of:

Does it apply to me?

ISO/IEC 27001 is a voluntary standard. Companies implement it because customers require certification, because they want a recognised framework for NIS2 or to manage their information security systematically.

Complass explains the requirements in its own words and refers to the clauses of the standard. For the certification audit you should own the standard yourself; you can store your own excerpts in the portal.

This overview does not replace legal advice. The legal or normative text is authoritative; in Complass you check applicability with guidance based on the references.

Legal basis

  • ISO/IEC 27001:2022Information security management systems – requirements
  • ISO/IEC 27002:2022Information security controls (guidance on Annex A)
  • § 30 BSIG§ 30 BSIG Risikomanagementmaßnahmen besonders wichtiger Einrichtungen und wichtiger Einrichtungen(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, geeignete, verhältnismäßige und wirksame technische und organisatorische Maßnahmen, die in Absatz 2 konkretisiert werden, zu ergreifen, um Störungen der Verfügbarkeit, Integrität und Vertraulichkeit der informationstechnischen Systeme, Komponenten und Prozesse, die sie für die Erbringung ihrer Dienste nutzen, zu vermeiden und …As of: 26.09.2026 · Source: gesetze-im-internet.deOpen original (gesetze-im-internet.de) ↗Under NIS2, European and international standards are to be taken into account

Key dates

There are no statutory deadlines for ISO/IEC 27001. The schedule is set by your certification audit or your customers’ requirements; you enter audit dates in the project plan, and the dashboard shows the countdown and whether you are on track.

How Complass helps

  • 9phases
  • 32guided steps
  • 48document templates
  • 93requirements in the catalogue
  • Nine phases to the certification audit

    Project start, context, leadership, planning with risk assessment, support, operation, evaluation, improvement and audit preparation.

  • Statement of Applicability

    All Annex A controls with applicability, justification, status and evidence, exportable as Excel or PDF.

  • Internal audit programme (9.2)

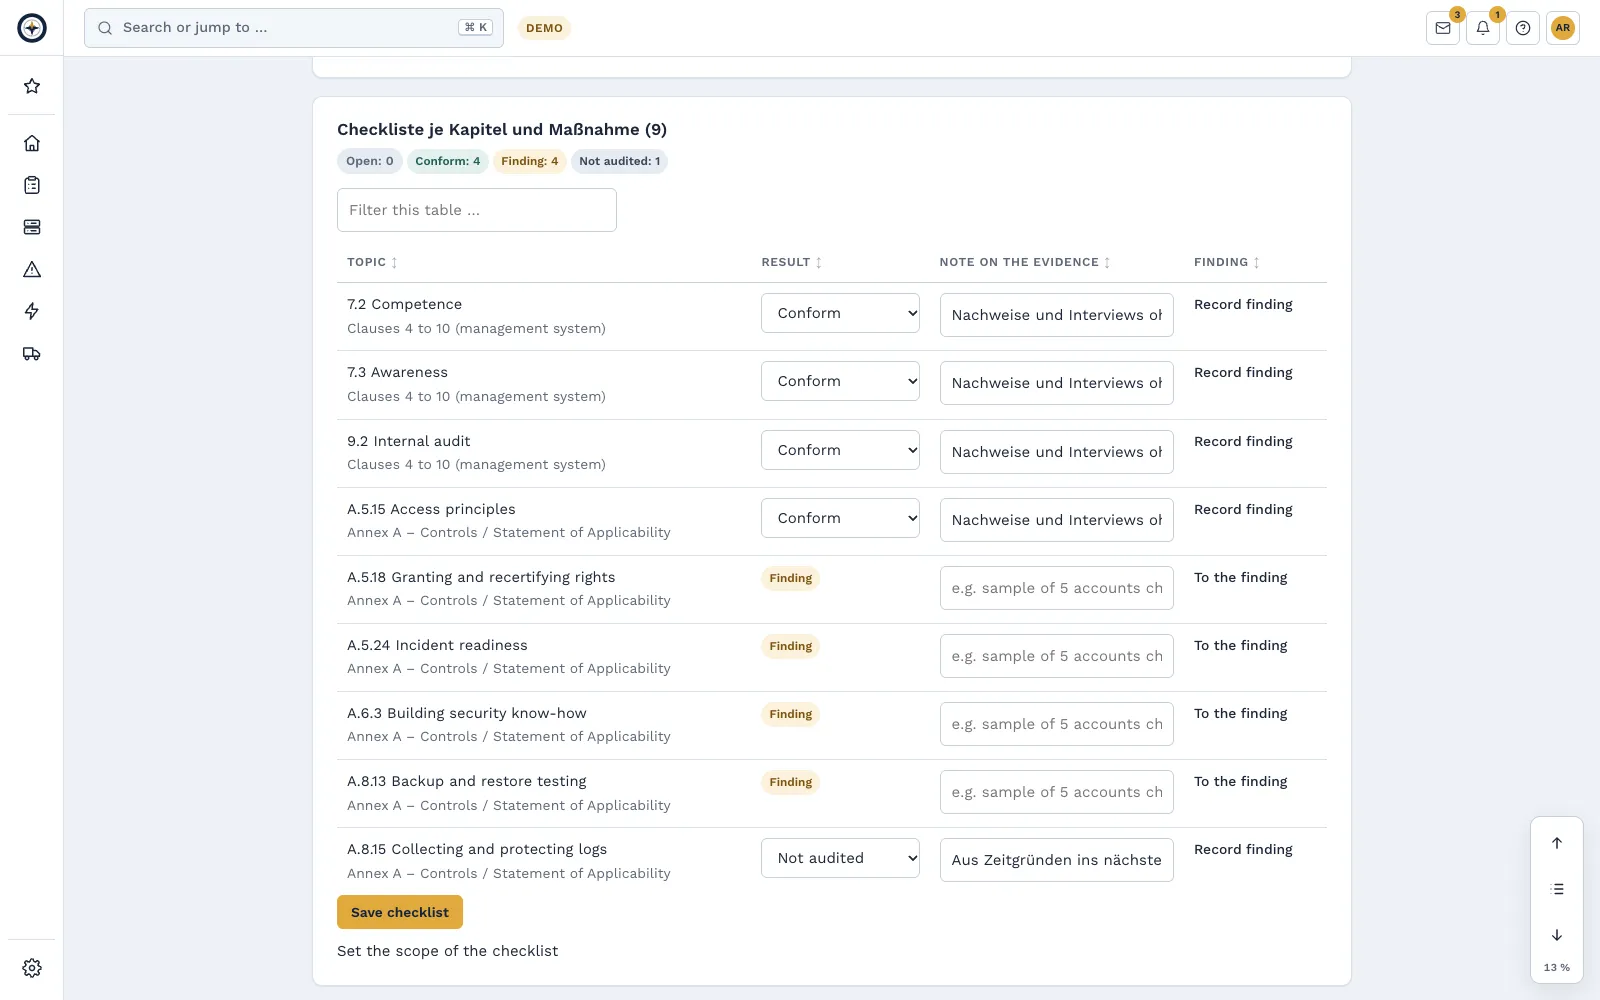
    Plan internal audits across the certification cycle, with an audit plan, a checklist per clause and Annex A control and an overview of what has already been audited.

  • All key documents

    Including scope, policy, risk assessment methodology, risk register, risk treatment plan, internal audit programme and management review.

  • Inventory and licences (A.5.9, A.5.32)

    Assets, software, licences and contracts with owners, deadlines and evidence in the asset management module, as the basis for the inventory and licensed use.

  • Use it several times

    Implemented controls also count for NIS2, IEC 62443 and the CRA through linking.

The phases in the module

  1. Project kick-off and preparation
  2. Context of the organization and scope
  3. Leadership and information security policy
  4. Planning: risk assessment, risk treatment and objectives
  5. Support: resources, competence, awareness and documentation
  6. Operation: implementing and controlling measures
  7. Performance evaluation: metrics, internal audit and management review
  8. Improvement: nonconformities and continual improvement
  9. Prepare for and pass the certification audit

Catalogue: Annex A – Controls / Statement of Applicability

Checklist of an internal audit with result per clause and control
Checklist per clause and Annex A control.

Matching modules

ISO 27001 / 27002 in Complass: what you need at a minimum

The first selection covers the requirements in Complass if your customers require them.

What you need at a minimum

If your customers require ISO 27001: this selection covers the requirements in Complass. It is preselected when you start a trial or order.

Portal size Start

  • ISO 27001 / 27002: Required by your customers? The framework then covers the requirements. Not a legal duty.
  • GDPR, AI Act and Whistleblower protection (HinSchG) (baseline protection): included
Price of the minimum selection
ItemNet price per month
Start S€179
ISO 27001 / 27002included
GDPR, AI Act and Whistleblower protection (HinSchG) (baseline protection)included
Total€179 net/month

With annual payment, 12 months minimum term. Monthly payment with a 15 % surcharge. All prices net plus VAT, as of 16 October 2026.

Adjust the selection in the price overview: minimum selection ISO 27001 / 27002

Frequently asked questions

Does Complass certify our ISMS?

No. Certification is carried out by an accredited certification body. Complass prepares you with documents, the Statement of Applicability and evidence.

Are the texts of the standard included?

No, standards are protected by copyright. Complass explains the requirements and refers to the clause; you can store your own excerpts from your licensed copy.

Try Complass with your own data

Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.