

Features included from Professional: Supplier Management, compare packages
Supplier Management
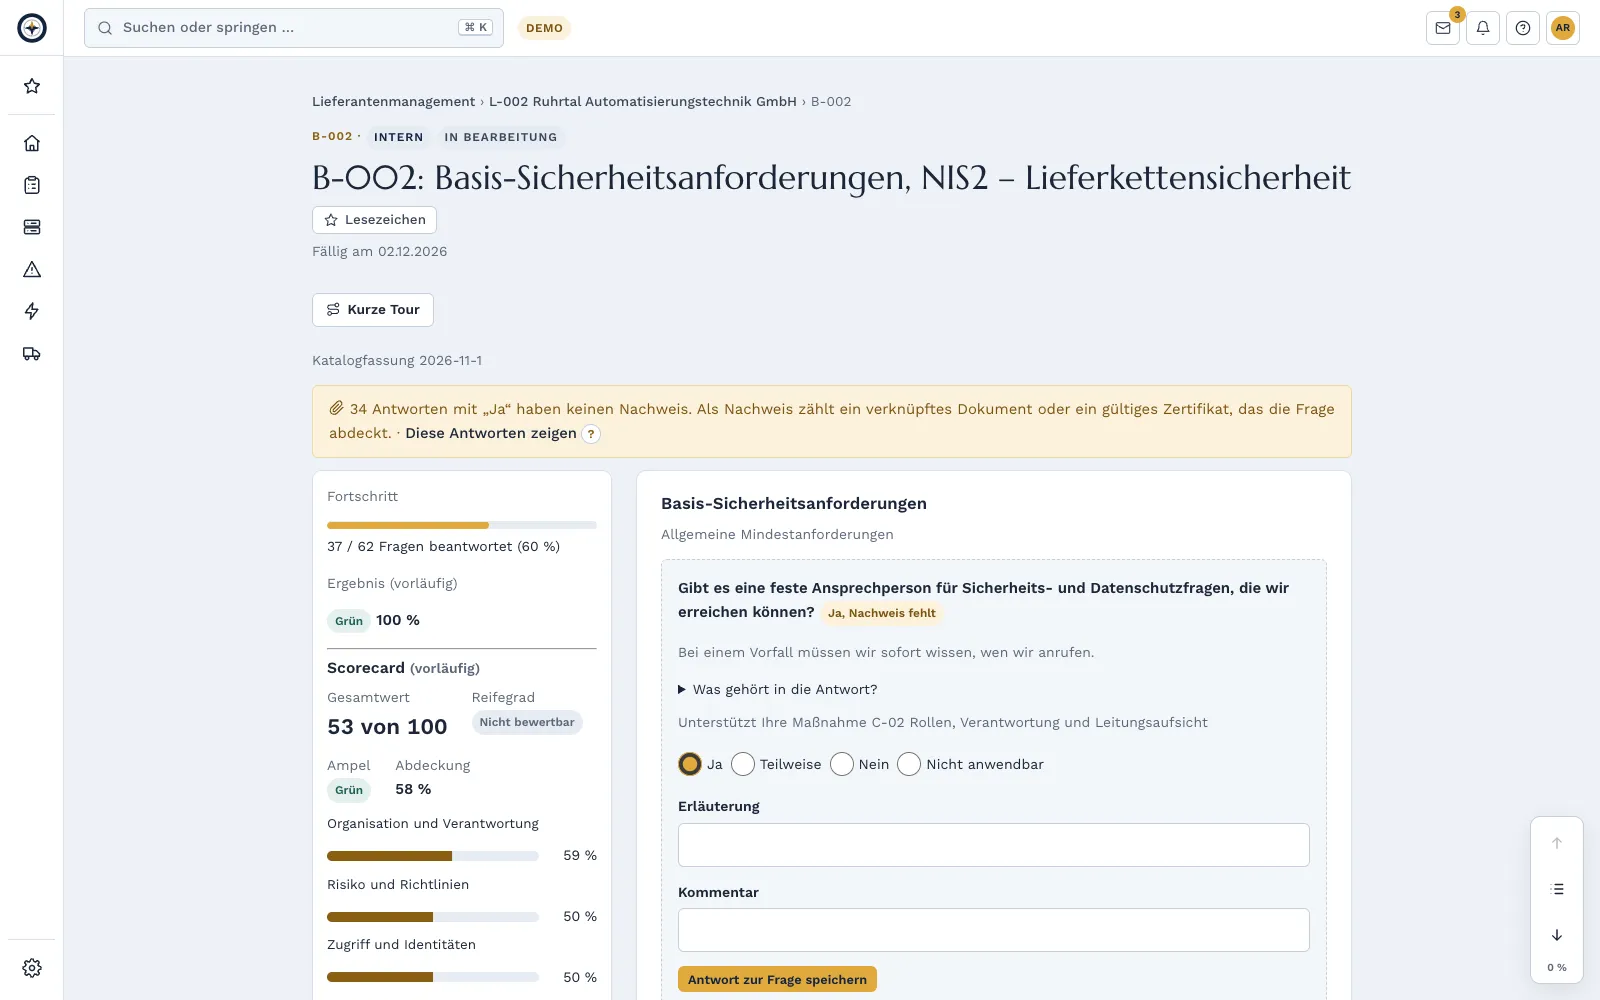
Supplier management where your suppliers take part: you invite, the supplier fills in the self-assessment and uploads evidence, you review and ask for more. The result feeds into risks, measures and the management cockpit.
Why
NIS2 requires security in the supply chain, ISO 27001 requires the management of supplier relationships, and the Cyber Resilience Act requires diligence for bought-in components. Anyone who grants integrators and maintenance providers access to their plants checks them under IEC 62443-2-4. Complass brings the matching questionnaires.
Legal and normative basis
- § 30 Abs. 2 Nr. 4 BSIG§ 30 BSIG Risikomanagementmaßnahmen besonders wichtiger Einrichtungen und wichtiger Einrichtungen(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, geeignete, verhältnismäßige und wirksame technische und organisatorische Maßnahmen, die in Absatz 2 konkretisiert werden, zu ergreifen, um Störungen der Verfügbarkeit, Integrität und Vertraulichkeit der informationstechnischen Systeme, Komponenten und Prozesse, die sie für die Erbringung ihrer Dienste nutzen, zu vermeiden und …Open original (gesetze-im-internet.de) ↗
- Art. 21 Abs. 2 lit. d NIS2-RichtlinieArticle 21 NIS 2 Directive Cybersecurity risk-management measures1. Member States shall ensure that essential and important entities take appropriate and proportionate technical, operational and organisational measures to manage the risks posed to the security of network and information systems which those entities use for their operations or for the provision of their services, and to prevent or minimise the impact of incidents on recipients of their services and on other …Open original (EUR-Lex) ↗
- Art. 28 DSGVOArticle 28 GDPR Processor1. Where processing is to be carried out on behalf of a controller, the controller shall use only processors providing sufficient guarantees to implement appropriate technical and organisational measures in such a manner that processing will meet the requirements of this Regulation and ensure the protection of the rights of the data subject. 2. The processor shall not engage another processor without prior specific …Open original (EUR-Lex – consolidated version incl. corrigenda) ↗
- ISO/IEC 27001:2022, A.5.19–A.5.23
- Art. 13 Abs. 5 CRAArticle 13 Cyber Resilience Act Obligations of manufacturers1. When placing a product with digital elements on the market, manufacturers shall ensure that it has been designed, developed and produced in accordance with the essential cybersecurity requirements set out in Part I of Annex I. 2. For the purpose of complying with paragraph 1, manufacturers shall undertake an assessment of the cybersecurity risks associated with a product with digital elements and take the outcome …Open original (EUR-Lex – OJ L 2024/2847, 20.11.2024, corrigenda incorporated: OJ L 2024/90780, 5.12.2024; OJ L 2025/90555, 2.7.2025; OJ L 2025/90828, 17.10.2025) ↗
- IEC 62443-2-4
Supply chain at the push of a button
Manufacturers release SBOM, VEX and security advisories for their products once and share them with the customers they authorise. You receive them right in the supplier record, with checksum and import, without questionnaire ping-pong.
How it works
- 1
Record and classify
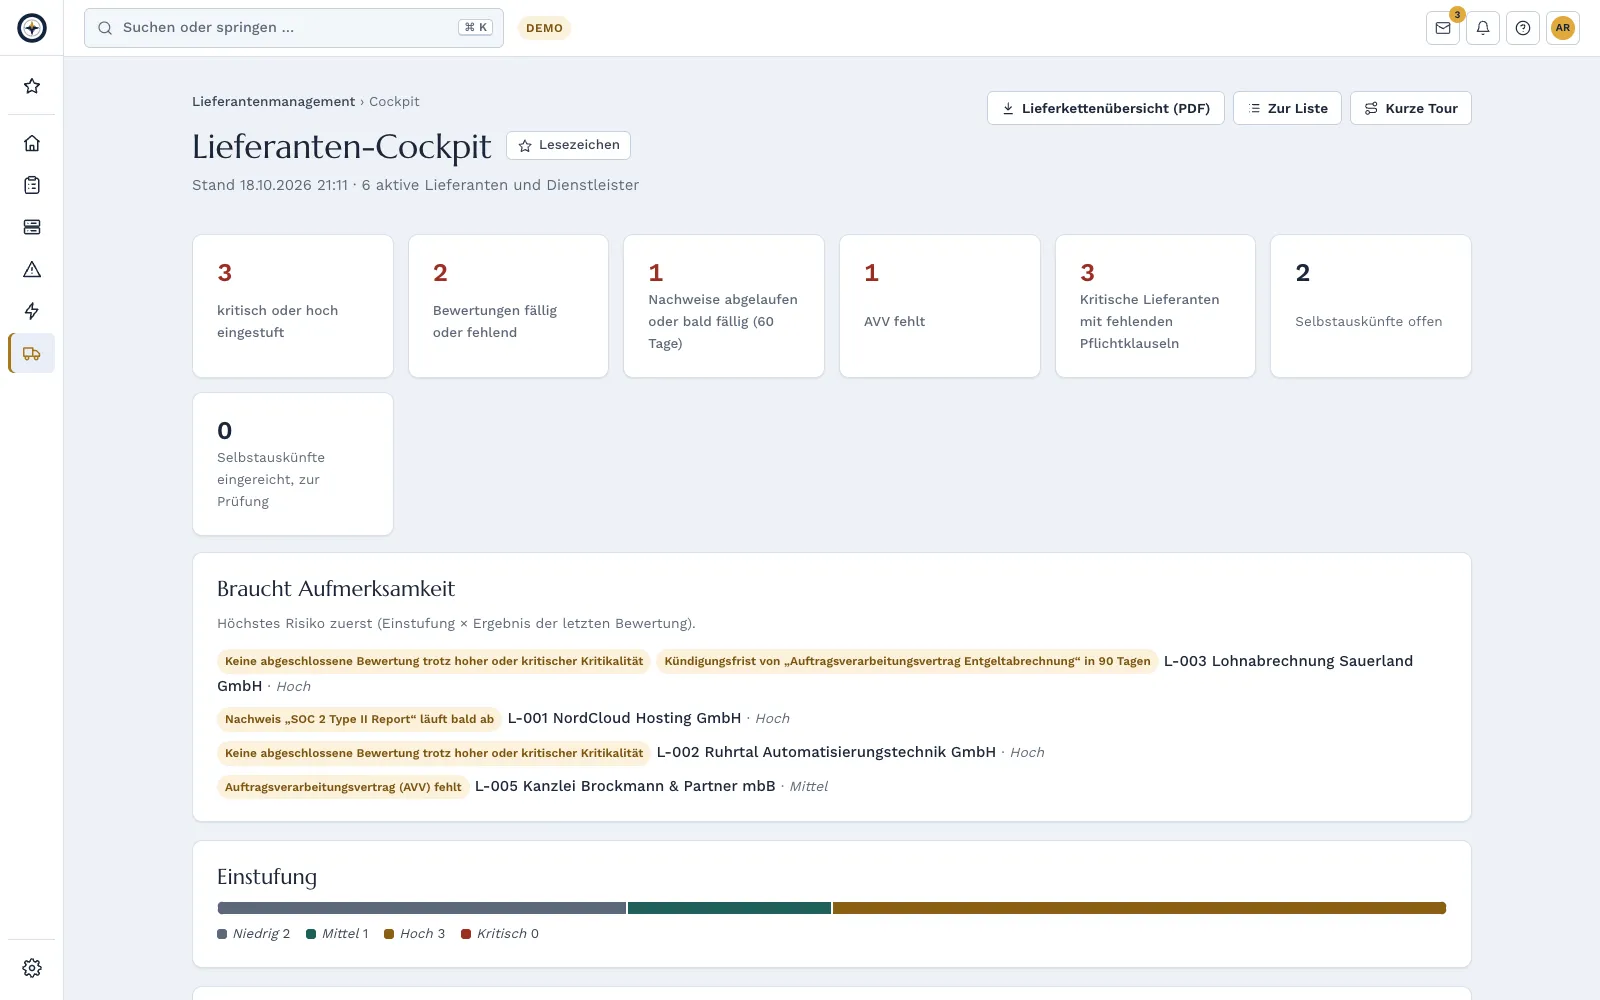
Create suppliers with contacts, contracts, the data processing agreement and evidence. Four questions on data access, plant access, the impact of an outage and replaceability yield the classification from low to critical. It determines the questionnaire and the review rhythm.
- 2
Invite
You choose the building blocks of the self-assessment and a deadline. The supplier receives an email with a link, without content.
- 3
Supplier responds
They answer the questions in their own, free account, upload evidence such as certificates or penetration test reports and submit. One account is enough for all their customers in Complass.
- 4
Review and act
Per answer “in order” or “request more”. Gaps become measures with a deadline or risks in the supply chain category. The result appears as a traffic light.
Questionnaires
Basic · NIS2 (supply chain under § 30 BSIG) · GDPR and the data processing agreement (Art. 28: technical and organisational measures, sub-processors, deletion) · ISO 27001 (Annex A 5.19–5.23) · CRA (for manufacturers of components and software) · IEC 62443-2-4 (for integrators and maintenance providers in OT) · your own questions
Questions in German and English. Certificates such as ISO 27001, TISAX or SOC 2 are stored as evidence with an expiry date; Complass reminds you before it runs out.
Connected throughout Complass
Management cockpit
Status of supply chain security at a glance.
Key figures and report
Assessed suppliers, red results and expired evidence in the management report.
Risks
A red result becomes a risk in the supply chain category with one click.
Measures and deadlines
Contract end, notice period, expiry of evidence and reassessment, also in the calendar subscription.
Asset inventory
Which systems depend on this supplier.
Permission profiles
Purchasing, IT security and data protection work on it, management reads along.
Supplier portal: for your suppliers
Free of charge for suppliers. Their own account with MFA or passkey. Suppliers only see the questionnaires and evidence you assign them. One account for several customers, with a customer switcher. They keep their answers once and reuse them for further customers. User interface and questions in German and English.
Exports: Supply chain overview as PDF, list as Excel or CSV, individual report per supplier as PDF and Word. Every export is recorded in the audit log.
Frequently asked questions
Do my suppliers have to pay anything?
No, supplier accounts are free of charge.
What if a supplier does not want to sign in?
You fill in the self-assessment on their behalf, for example after a conversation, and upload the evidence yourself.
Do suppliers see other data from my company?
No, only the tasks you assign them.
Can a supplier use their answers for several customers?
Yes. They use one account for all their customers, keep their answers once in their profile and take them over into another customer’s questionnaire instead of answering again.
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.