

Framework In preparation
Energy Industry Act (EnWG) and IT security catalogue
Applies in Germany only (German law). Network operators, operators of energy facilities and operators of digital energy services implement IT security under sections 5c to 5e of the German Energy Industry Act (EnWG), in the network and in the control systems. Complass guides you from clarifying your role through the applicable IT security catalogue to incident reporting, evidence and management duties, and adds the new catalogue of the Federal Network Agency as soon as it is fixed.

In preparation The Energy Industry Act (EnWG) and IT security catalogue module is in preparation and cannot be booked yet. We will only name a start date and a price once both are fixed. On this page we describe what the module is to cover. We are happy to show you the current state in a demo. Request a demo · Send an enquiry
What is the IT security catalogue under the EnWG?
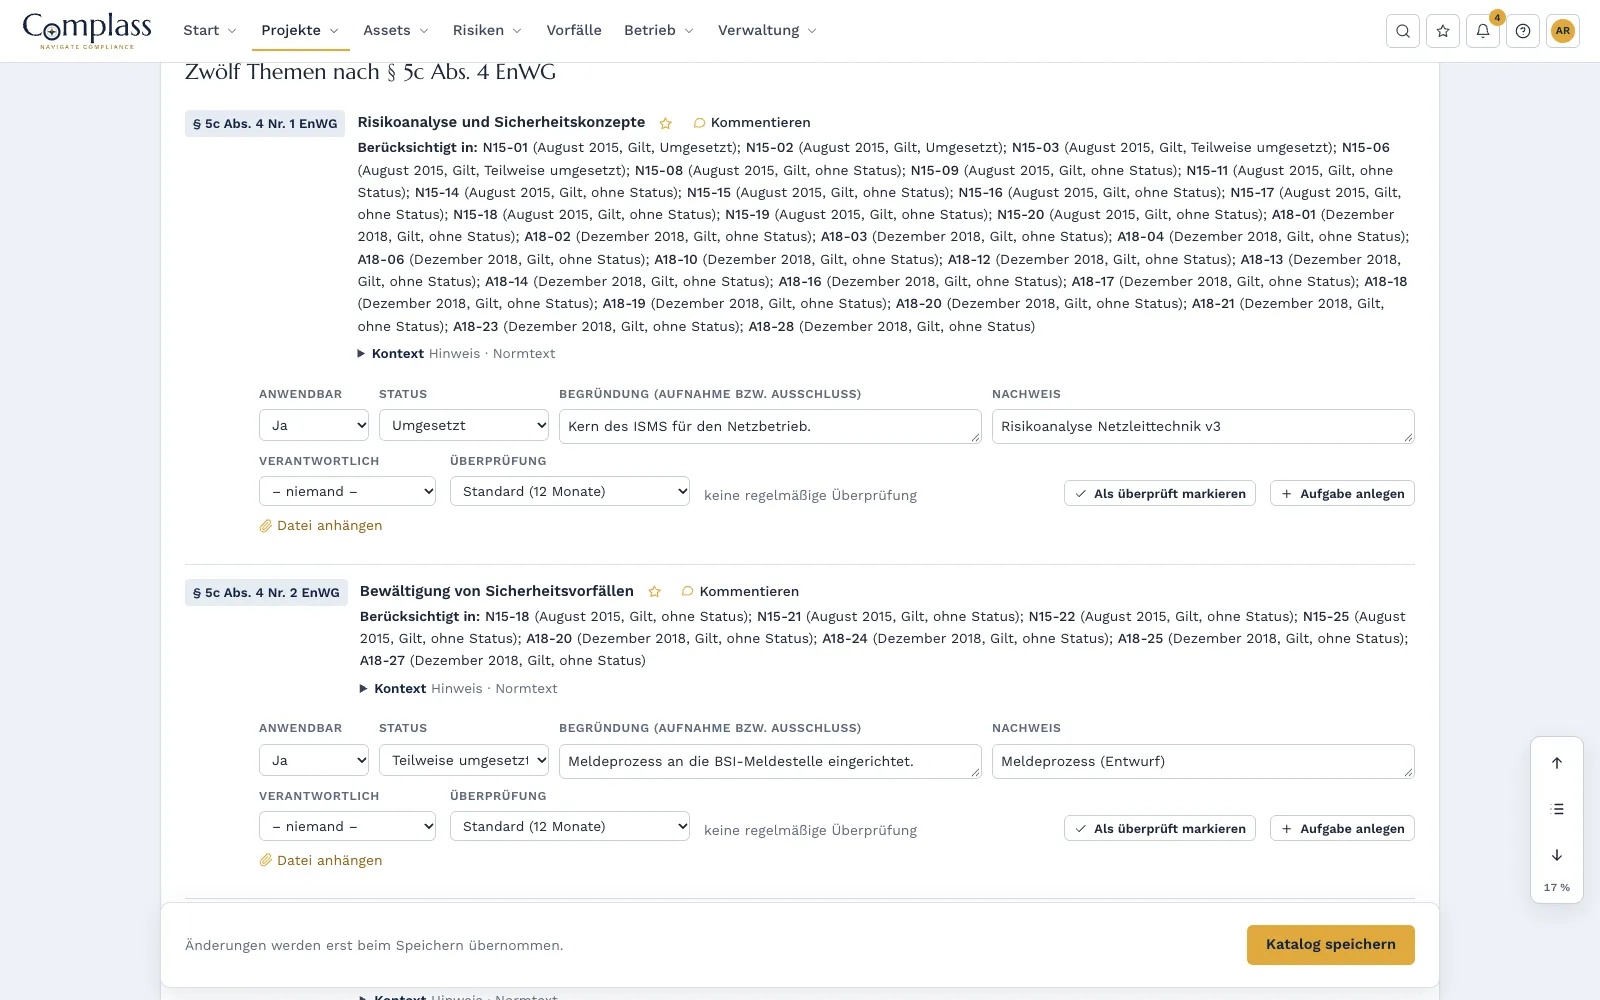
Applies in Germany only (German law). Since 6 December 2025, sections 5c to 5e of the German Energy Industry Act (EnWG) govern IT security in the energy sector. What operators must implement in detail is set by the Federal Network Agency (BNetzA), in agreement with the BSI, in an IT security catalogue. The act names twelve topics that every catalogue must contain at least, from risk analysis through attack detection to multi-factor authentication. In addition there are the reporting of significant security incidents, registration, documentation and the responsibility of management.
Content as of:
Does it apply to me?
The EnWG distinguishes three roles. For network operators it applies regardless of size; operators of energy facilities and digital energy services are covered if they are important or particularly important entities under the German BSI Act.
| Role | Covered if | What applies today |
|---|---|---|
| Electricity or gas network operators | You operate an energy supply network, no size threshold | IT security catalogue for network operators, August 2015 |
| Operators of energy facilities, e.g. generation or storage | Energy facility connected to the network and important or particularly important entity under section 28 BSIG | IT security catalogue for energy facilities, December 2018 |
| Digital energy services, e.g. aggregators | Service on an energy facility connected to the network and important or particularly important entity under section 28 BSIG | No BNetzA catalogue yet. Aggregators formerly covered by section 8a BSIG (old version) continue to implement the BDEW “B3S Aggregatoren”. |
Entities subject to sections 5c to 5e EnWG are exempt from most duties of the BSI Act; classification and registration remain. If municipal utilities also run water, waste water or other lines of business from Annex 1 or 2 of the BSI Act (multi-utility), the BSI Act applies to them. In Complass you manage these lines of business in a NIS2 project and link shared evidence. Telecommunications services are governed by the Telecommunications Act (TKG).
This overview does not replace legal advice. The legal or normative text is authoritative; in Complass you check applicability with guidance based on the references.
Legal basis
- § 5c EnWG§ 5c EnWG IT-Sicherheit im Anlagen- und im Netzbetrieb, Festlegungskompetenz(1) Die folgenden Betreiber haben für die genannten Systeme einen angemessenen Schutz gegen Bedrohungen zu gewährleisten: - 1. der Betreiber eines Energieversorgungsnetzes für Telekommunikationssysteme und für elektronische Datenverarbeitungssysteme, die für den sicheren Betrieb des Energieversorgungsnetzes notwendig sind, - 2. der Betreiber einer Energieanlage, der eine besonders wichtige Einrichtung nach § 28 …Open original (gesetze-im-internet.de) ↗IT security, roles, catalogue and its twelve minimum topics
- § 5d EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗Documentation, contact person, reporting and registration
- § 5e EnWG§ 5e EnWG Umsetzungs-, Überwachungs- und Schulungspflicht für Geschäftsleitungen(1) Die Geschäftsleitung eines Betreibers nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 ist verpflichtet, die Anforderungen des IT-Sicherheitskatalogs umzusetzen und die Umsetzung zu überwachen. (2) Eine Geschäftsleitung eines Betreibers nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3, die ihre Pflichten nach Absatz 1 verletzt, haftet ihrer Einrichtung für einen schuldhaft verursachten Schaden nach den auf die Rechtsform der …Open original (gesetze-im-internet.de) ↗Duties of management
- § 28 BSIG§ 28 BSIG Besonders wichtige Einrichtungen und wichtige Einrichtungen(1) Als besonders wichtige Einrichtung gelten - 1. Betreiber kritischer Anlagen, - 2. qualifizierte Vertrauensdiensteanbieter, Top Level Domain Name Registries oder DNS-Diensteanbieter, - 3. Anbieter öffentlich zugänglicher Telekommunikationsdienste oder Betreiber öffentlicher Telekommunikationsnetze, die - a) mindestens 50 Mitarbeiter beschäftigen oder - b) einen Jahresumsatz und eine Jahresbilanzsumme von jeweils …Open original (gesetze-im-internet.de) ↗Classification as an important or particularly important entity, exemption under subsection 5
- § 32 BSIG§ 32 BSIG Meldepflichten(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, folgende Informationen an eine vom Bundesamt und dem Bundesamt für Bevölkerungsschutz und Katastrophenhilfe eingerichtete gemeinsame Meldestelle zu melden: - 1. unverzüglich, spätestens jedoch innerhalb von 24 Stunden nach Kenntniserlangung von einem erheblichen Sicherheitsvorfall, eine frühe Erstmeldung, in der angegeben wird, ob der …Open original (gesetze-im-internet.de) ↗Reporting obligations and deadlines
- Section 11(1a) and (1b) EnWG, old versionBasis of the two catalogues in force (2015 and 2018)
What applies today and what may come in 2027
- Sections 5c to 5e EnWG in force (NIS2 Implementation Act). Section 11(1a) to (1g) EnWG, old version, no longer apply.
- Deadline for registration with the BSI for network operators that are not important or particularly important entities · § 5d Abs. 4 EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗
- Today Until a new catalogue is published, the catalogues of August 2015 (networks) and December 2018 (energy facilities) remain in force. Existing attack detection systems must continue to be operated. Checked on 10 October 2026.
- 24 hours / 72 hours / one month Significant security incidents to the BSI reporting office: early warning, incident notification, final report · § 5d Abs. 3 EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗ with § 32 BSIG§ 32 BSIG Meldepflichten(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, folgende Informationen an eine vom Bundesamt und dem Bundesamt für Bevölkerungsschutz und Katastrophenhilfe eingerichtete gemeinsame Meldestelle zu melden: - 1. unverzüglich, spätestens jedoch innerhalb von 24 Stunden nach Kenntniserlangung von einem erheblichen Sicherheitsvorfall, eine frühe Erstmeldung, in der angegeben wird, ob der …Open original (gesetze-im-internet.de) ↗
- Without undue delay Submit the documentation to the Federal Network Agency: network operators always, operators of energy facilities and digital energy services as particularly important entities (professional assessment, not legal advice) · § 5d Abs. 1 Satz 2 EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗
- Autumn 2026 Consultation on a joint catalogue for networks, energy facilities and digital energy services, planned according to the Federal Network Agency
- 1 January 2027 (draft) Start of application according to the consultation draft. The new catalogue has not been fixed yet; the Federal Network Agency names no date on its procedure page.
We check the status at the Federal Network Agency before every release. When a new catalogue is fixed, Complass adds it as a new edition; your assessments of the twelve topics are kept.
What the module is to cover
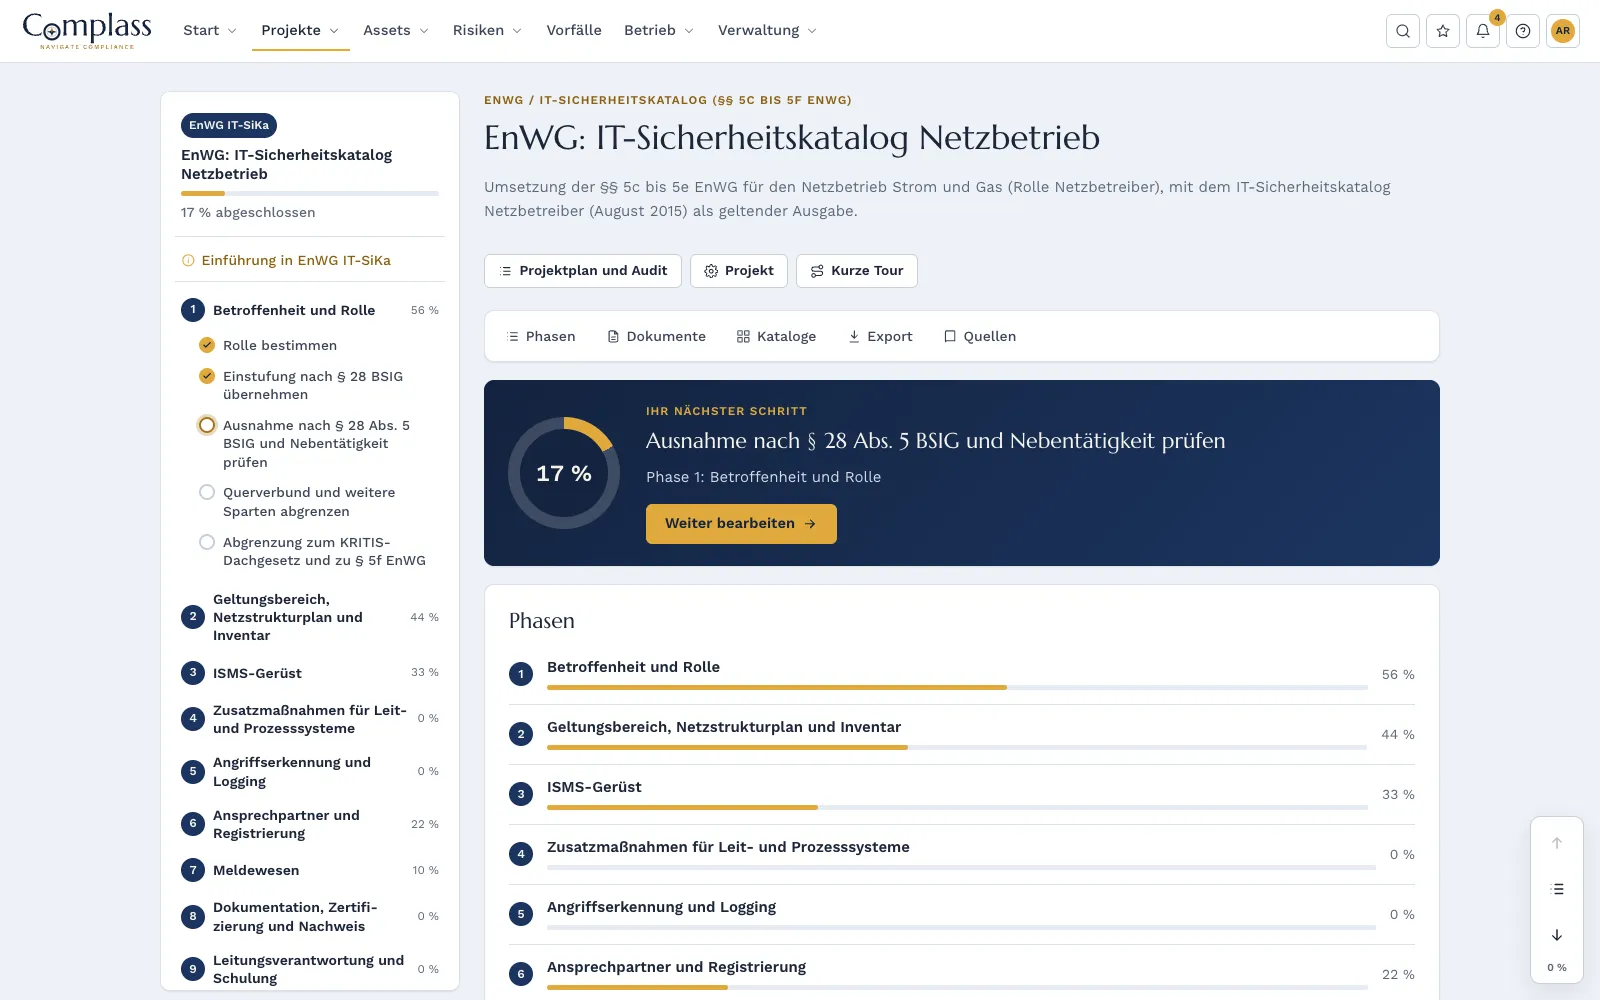
- 10phases
- 30guided steps
- 8document templates
- 77requirements in the catalogue
Twelve topics that stay
You assess the twelve topics of section 5c(4) EnWG once. The requirements of the 2015 and 2018 catalogues are linked to them. When the new catalogue comes, Complass adds it as a new edition without you having to start over.
The catalogue that applies to your role
Network operators work with the 2015 catalogue, operators of energy facilities with the 2018 catalogue, each with the requirements in their original wording and the source. Digital energy services use the twelve topics as their basis.
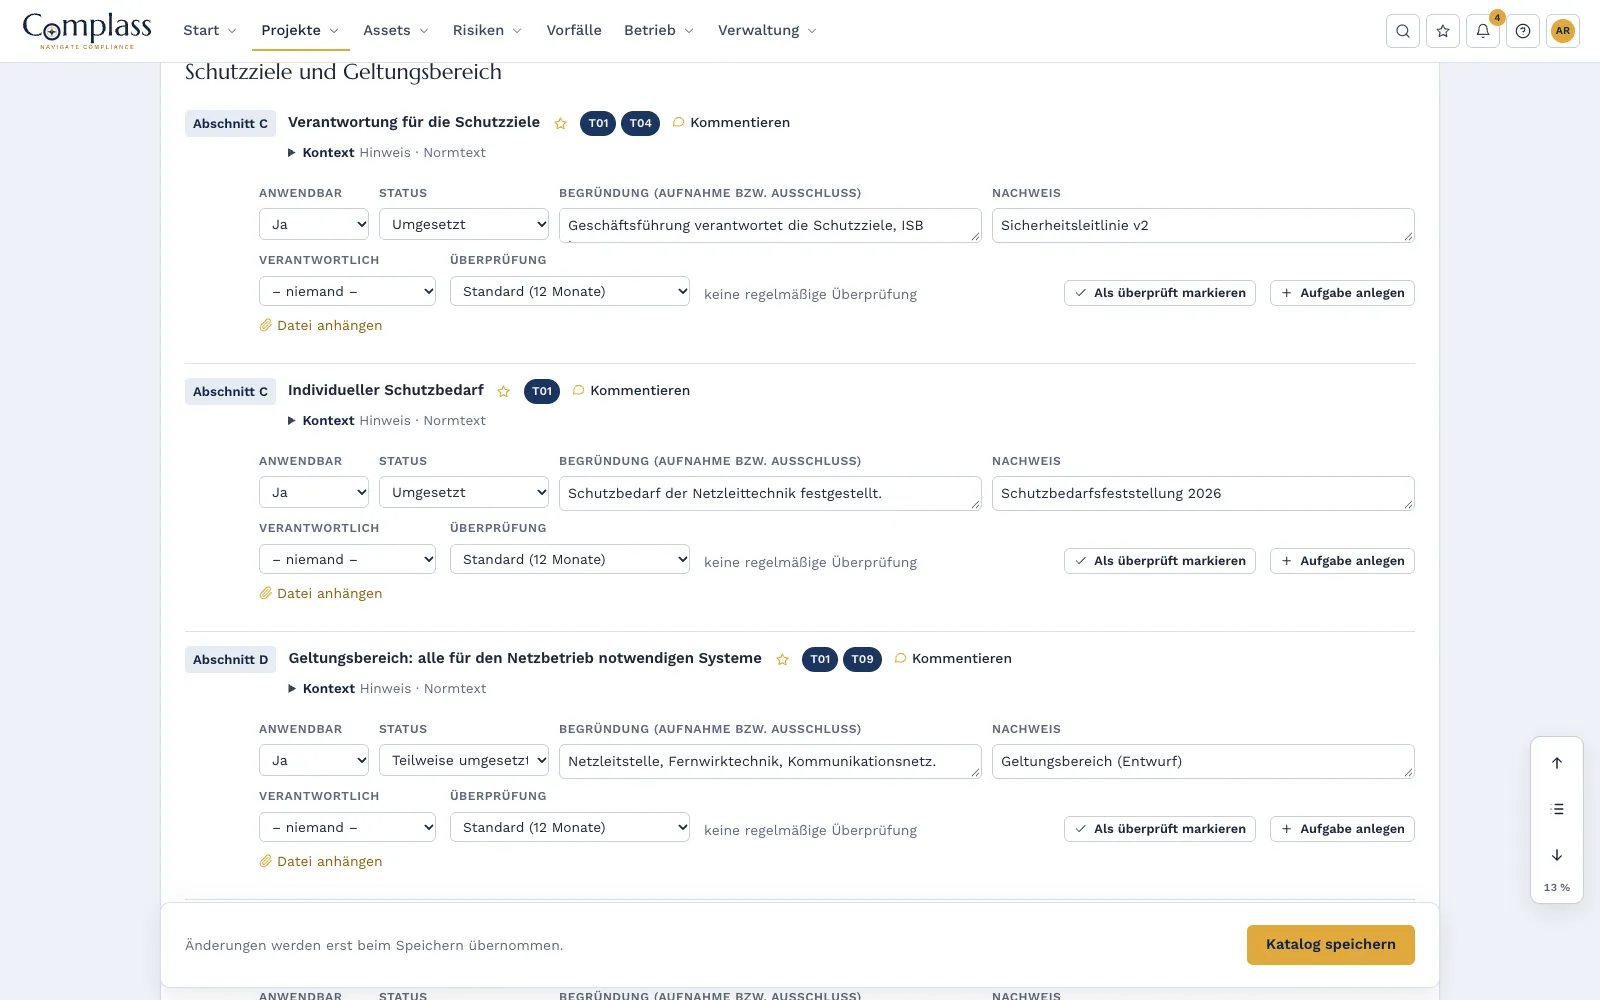
Network structure plan, inventory and control systems
Scope, network structure plan and systems in asset management, zones and remote access for control and process systems.
Attack detection and logging
Concept for attack detection systems with monitored systems, responsibilities and response to alerts.
Reports to the BSI reporting office
Reporting process with the deadlines of 24 hours, 72 hours and one month, incidents in the incident module with a countdown, distinction from reports under the KRITIS Umbrella Act.
Multi-utility with NIS2 in one portal
You manage further lines of business in the NIS2 project. You link shared evidence instead of maintaining it twice.
Management and training
Management duties under section 5e EnWG with learning blocks for specialists and for management.
The phases in the module
- Applicability and role
- Scope, network structure plan and inventory
- ISMS skeleton
- Additional measures for control and process systems
- Attack detection and logging
- Contact person and registration
- Incident reporting
- Documentation, certification and evidence
- Management responsibility and training
- Supply chain and critical functions
Catalogue: Minimum contents of the IT security catalogue (section 5c(4) EnWG)
Matching modules
Asset management
IT and OT assets in one place, agentless capture, with SBOM, vendor advisories, end of support, licence reconciliation, identities, relationships and zones per IEC 62443-3-2.
Learn moreIncident management
Record incidents, check reporting obligations under NIS2, the CRA and the GDPR and track the reporting deadlines with a countdown.
Learn moreRisk management
Risk register with qualitative or quantitative assessment, risk appetite and treatment plan, linked to assets, vulnerabilities and incidents.
Learn moreSupplier Management
Classify suppliers, request self-assessments and evidence directly from the supplier, review them and ask for more. With questionnaires for NIS2, GDPR, ISO 27001, the CRA and IEC 62443-2-4.
Learn moreFrequently asked questions
When can the module be booked?
The module is in preparation. We will only name a date once it is fixed. Get in touch: we will show you the current state and how you can start in Complass today with ISO/IEC 27001 or NIS2.
Does the EnWG or the BSI Act apply to us?
For network operation and for energy facilities of important or particularly important entities, sections 5c to 5e EnWG apply; most duties of the BSI Act do not apply to them. Classification and registration under the BSI Act remain. Further lines of business such as water or waste water are subject to the BSI Act. If the energy facility is only a secondary activity in relation to the business as a whole, the BSI Act applies as well.
Which IT security catalogue applies at the moment?
For network operators the catalogue of August 2015, for operators of energy facilities the catalogue of December 2018. According to the Federal Network Agency, both remain in force until a new catalogue is published. Status checked: 10 October 2026.
What changes in 2027?
The Federal Network Agency, together with the BSI, is revising the catalogues into one catalogue that is also to apply to digital energy services. The consultation draft names 1 January 2027 as the start of application. This has not been fixed yet. Your work on the twelve topics of section 5c(4) EnWG counts in any case, because every catalogue must contain them.
We are an aggregator. What do we do until the new catalogue?
If you were previously covered by section 8a BSIG (old version), continue to implement the BDEW “B3S Aggregatoren”. Otherwise build an ISMS under ISO/IEC 27001 and orient yourself by the twelve topics. In Complass you assess these topics and add the new catalogue as soon as it is fixed.
To whom do we report a security incident?
To the BSI reporting office: an early warning within 24 hours, an incident notification within 72 hours and a final report one month later at the latest. If the incident is relevant to the security of energy supply, the BSI forwards the report to the Federal Network Agency (section 5d(5) EnWG).
Does Complass replace a legal review?
No. Complass structures the applicability check, obligations and evidence based on the legal text and the catalogues; the legal assessment of the individual case remains with you.
Does the EnWG apply to your company?
The free applicability check gives you an initial assessment in a few minutes of whether you are a network operator, an operator of energy facilities or a digital energy service and which frameworks apply.
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.