

Features included from Professional: Privacy operations, compare packages
Privacy operations
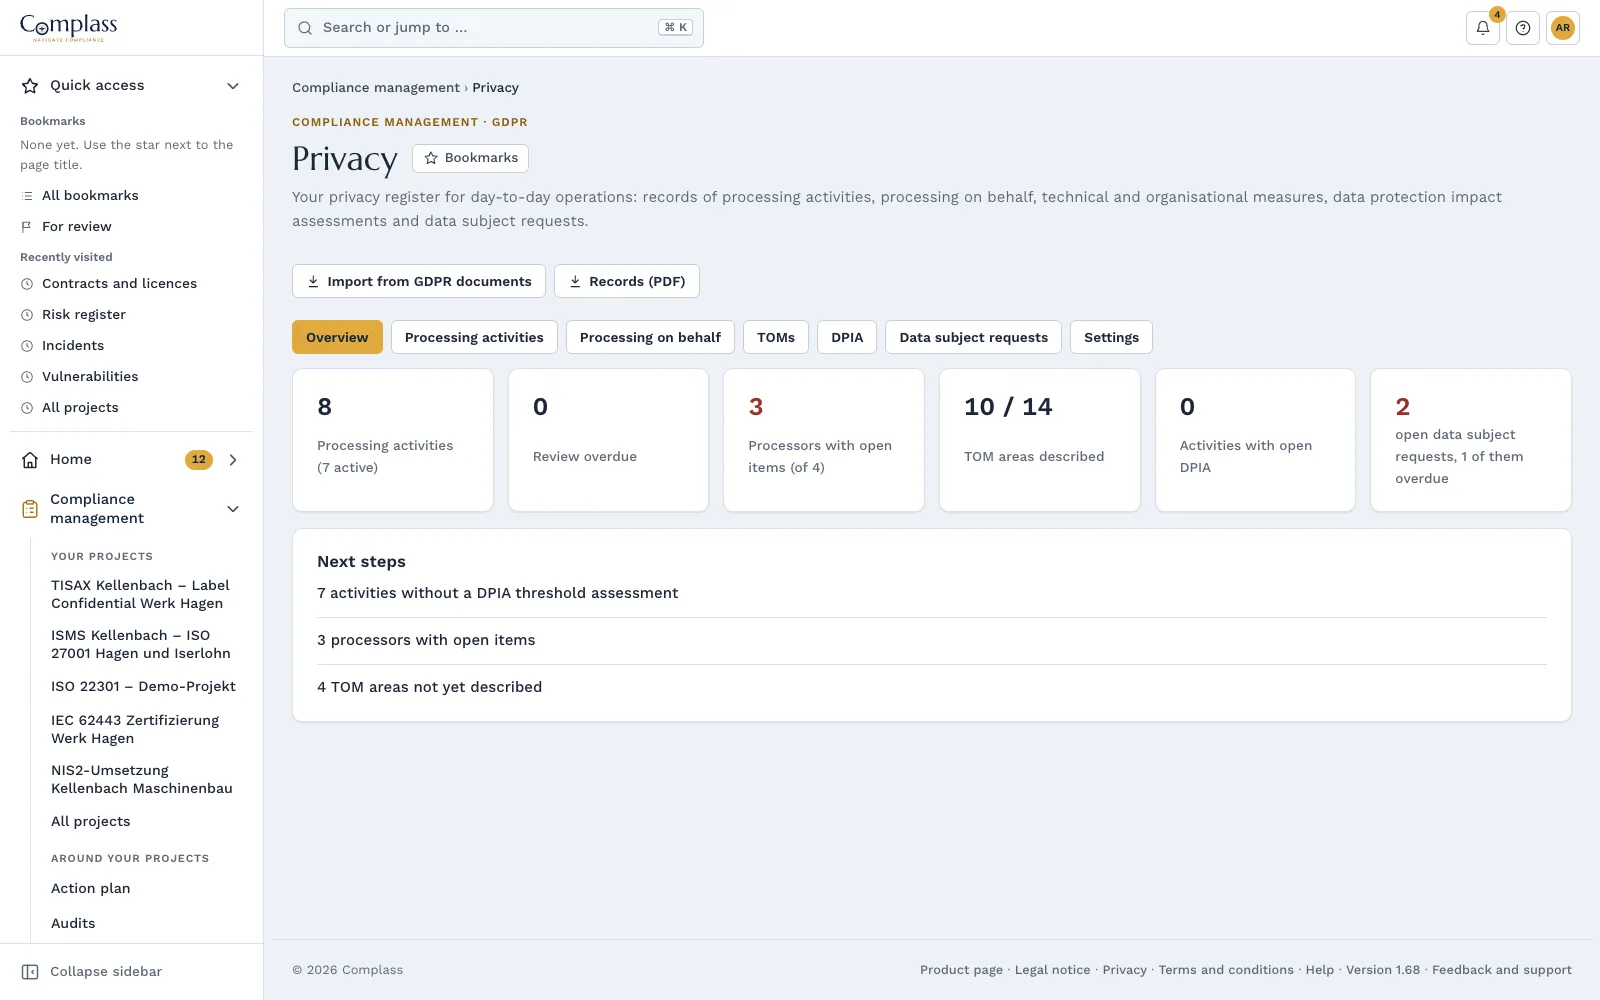
One privacy register for day-to-day operations: records, processors, TOMs, impact assessments and data subject requests, linked and with deadlines.
The supervisory authority asks for the records of processing activities, a customer asks for the TOM list, an access request has a one-month deadline. If all this sits in scattered spreadsheets, every one of these questions becomes a project.
How Complass helps
Records of processing activities
All details under Art. 30 GDPR, as controller and as processor: purpose, legal basis, data subjects, data, recipients, third countries, retention periods and TOMs. With review dates and export as PDF, Word or Excel. You take over existing tables from the GDPR project once, with a preview. Complass shows missing mandatory details and contradictions in the legal basis.
Processors in both directions
Service providers working for you and customers you work for, with subprocessors and third-country transfers. Linked to the supplier and the data processing agreement; Complass shows open points such as a missing contract or a transfer without safeguards. Complass flags processing locations and sub-processors in third countries without a recorded transfer.
TOMs from one source with the ISMS
14 areas under Art. 32 GDPR with description and status. For each area you see the linked controls and their status from your projects, for example ISO 27001 or NIS2. The TOM list is available as PDF or Word file, for example as an annex to the data processing agreement.
Guided data protection impact assessment
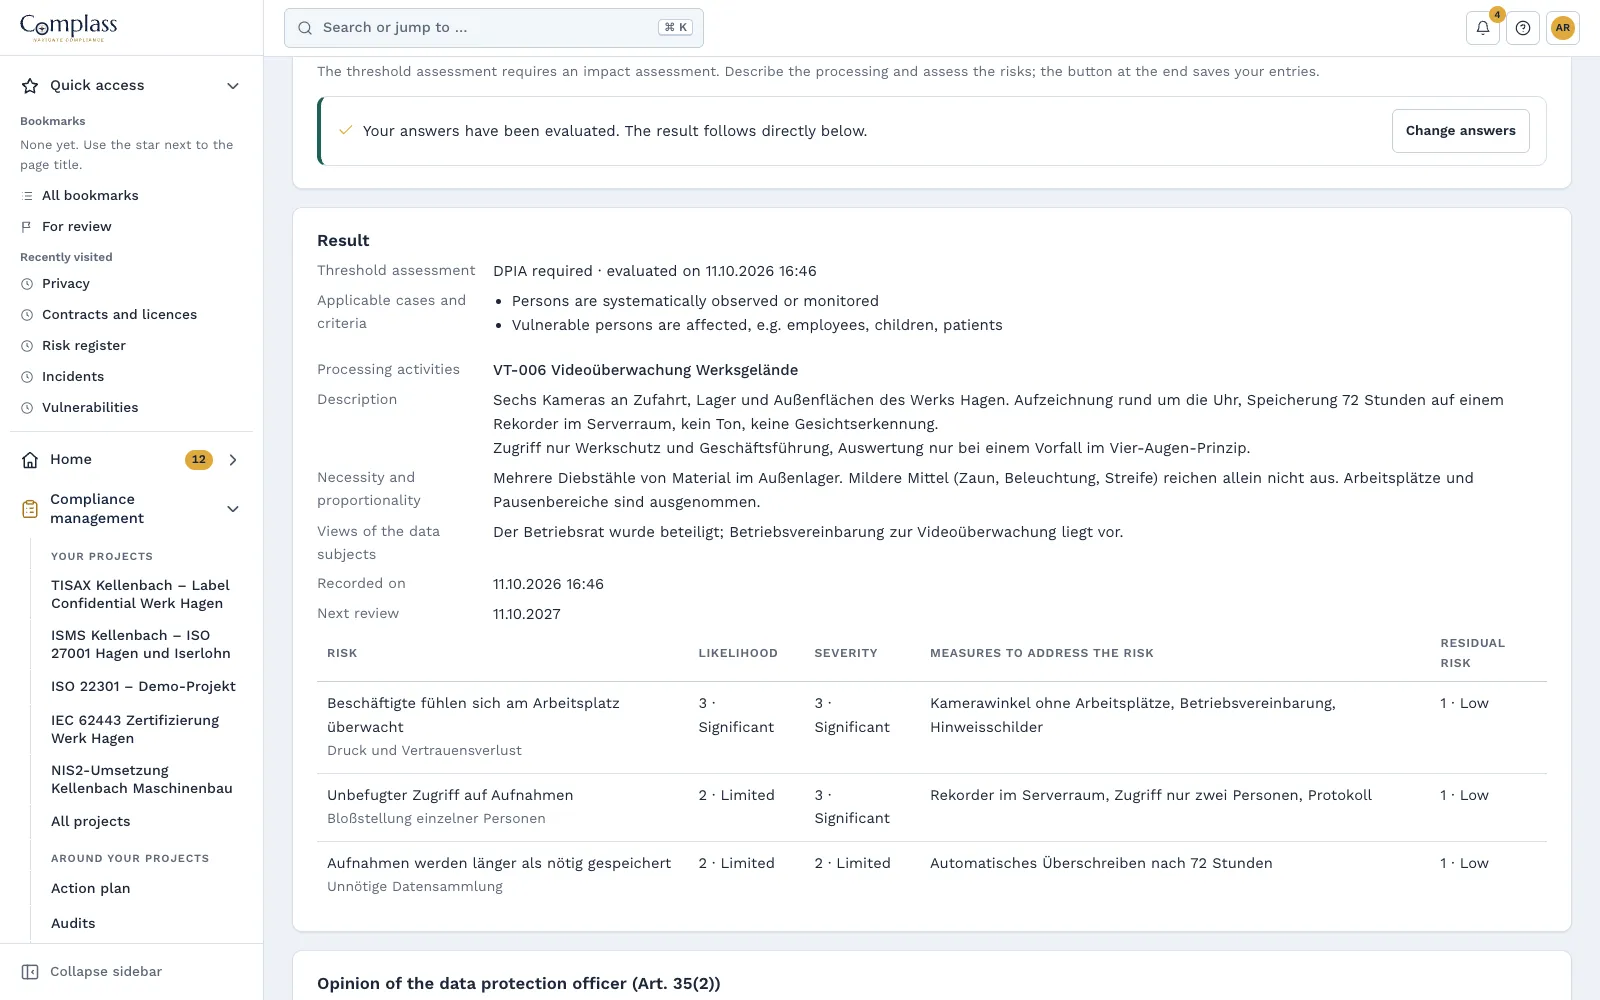
Step by step from the threshold check with the cases under Art. 35(3) and the nine criteria of the European guidelines via risks and mitigating measures to the opinion of the data protection officer and approval. Report as PDF or Word.
Data subject requests with the one-month deadline
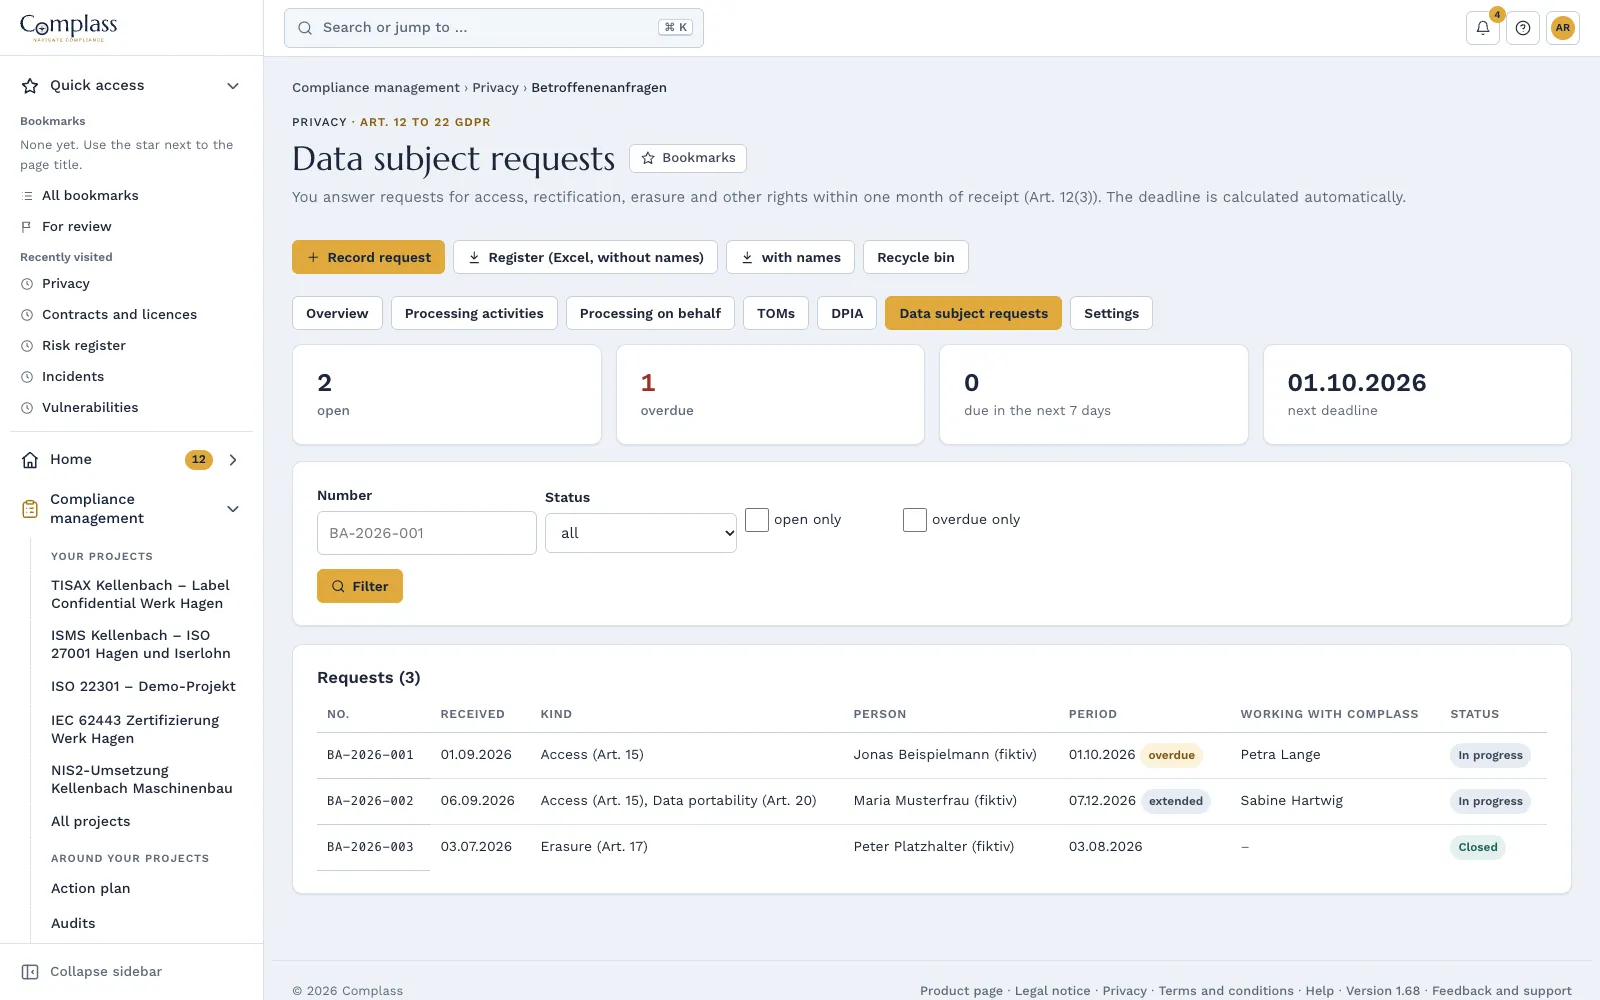
Complass calculates the deadline from receipt; if it falls on a weekend, the following Monday applies. Extension only with a reason, reminders seven days before the deadline and when it is exceeded. Name and contact are deleted automatically after a configurable period.
Connected with incidents and deadlines
Personal data breaches stay in incident management and are linked to the affected processing activities. Reviews and deadlines appear in the deadlines calendar, open points on the dashboard and as figures in the management cockpit.
Legal and normative basis
- Art. 30 GDPRArticle 30 GDPR Records of processing activities1. Each controller and, where applicable, the controller's representative, shall maintain a record of processing activities under its responsibility. That record shall contain all of the following information: - (a) the name and contact details of the controller and, where applicable, the joint controller, the controller's representative and the data protection officer; - (b) the purposes of the processing; - (c) a …Open original (EUR-Lex – consolidated version incl. corrigenda) ↗
- Art. 28 GDPRArticle 28 GDPR Processor1. Where processing is to be carried out on behalf of a controller, the controller shall use only processors providing sufficient guarantees to implement appropriate technical and organisational measures in such a manner that processing will meet the requirements of this Regulation and ensure the protection of the rights of the data subject. 2. The processor shall not engage another processor without prior specific …Open original (EUR-Lex – consolidated version incl. corrigenda) ↗
- Art. 32 GDPRArticle 32 GDPR Security of processing1. Taking into account the state of the art, the costs of implementation and the nature, scope, context and purposes of processing as well as the risk of varying likelihood and severity for the rights and freedoms of natural persons, the controller and the processor shall implement appropriate technical and organisational measures to ensure a level of security appropriate to the risk, including inter alia as …Open original (EUR-Lex – consolidated version incl. corrigenda) ↗
- Art. 35 GDPRArticle 35 GDPR Data protection impact assessment1. Where a type of processing in particular using new technologies, and taking into account the nature, scope, context and purposes of the processing, is likely to result in a high risk to the rights and freedoms of natural persons, the controller shall, prior to the processing, carry out an assessment of the impact of the envisaged processing operations on the protection of personal data. A single assessment may …Open original (EUR-Lex – consolidated version incl. corrigenda) ↗
- Art. 12 GDPRArticle 12 GDPR Transparent information, communication and modalities for the exercise of the rights of the data subject1. The controller shall take appropriate measures to provide any information referred to in Articles 13 and 14 and any communication under Articles 15 to 22 and 34 relating to processing to the data subject in a concise, transparent, intelligible and easily accessible form, using clear and plain language, in particular for any information addressed specifically to a child. The information shall be provided in …Open original (EUR-Lex – consolidated version incl. corrigenda) ↗
- DPIA guidelines (WP248 rev.01)
Read the privacy operations whitepaper
This page describes Complass features and is not legal advice.
Frequently asked questions
Is privacy operations included in the package?
Privacy operations is a bookable module and included in the Professional and Premium packages. The GDPR framework with phases, templates and obligations catalogue remains included in every package.
How does the register differ from the GDPR framework?
The framework guides you through implementation: phases, templates and the obligations catalogue. The register is the ongoing operation afterwards: one record per company, even with several projects, with reviews, deadlines and exports. Tables you have already maintained in the project are taken over once.
Who sees the names in data subject requests?
Only people with the separate right for data subject requests, by default the administrators. The register export comes without names, with names only on explicit choice. In a support session, name and contact are hidden.
Can we take the register over into other tools?
Yes, read-only: through the REST API with the scope “privacy:read”, reporting and GRC tools read the register as metadata, without personal content. Only administrators issue the key, and every call is in the log. The API is available from the Professional package.
Does Complass replace the data protection officer?
No. Complass structures, reminds and documents. Assessments, approvals and the advice of the data protection officer remain with you.
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.