

Framework
IT security guideline under Section 390 SGB V (KBV and KZBV)
Every practice that takes part in statutory medical or dental care must implement the IT security guideline. Complass shows you which requirements apply to your practice and guides you step by step to robust documentation, even without an IT department of your own.

What does the IT security guideline cover?
Section 390 SGB V obliges the National Association of Statutory Health Insurance Physicians (KBV) and the National Association of Statutory Health Insurance Dentists (KZBV) to set binding IT security requirements for practices. Both have published a guideline with the same structure and numbering. It specifies the state of the art under Art. 32 GDPR for practices, is agreed with the BSI and reviewed every year.
Content as of:
Does it apply to me?
The guideline is binding for all providers taking part in statutory medical and dental care. Medical and psychotherapy practices implement the KBV version, dental practices the KZBV version, medical care centres (MVZ) and group practices one or both depending on their specialties. It does not apply to statutory medical care in hospitals where measures under Section 391 SGB V are already in place.
Which requirements apply depends on the number of people permanently involved in data processing, including medical and dental assistants and trainees: Annex 1 (50 requirements) and Annex 5 on the telematics infrastructure (9) apply to all, Annex 2 (10) from 6 people, Annex 3 (17) from more than 20 people, Annex 4 (6) for large medical equipment. Each requirement applies only if its target object is used in the practice. Larger medical care centres can additionally fall under NIS2.
This overview does not replace legal advice. The legal or normative text is authoritative; in Complass you check applicability with guidance based on the references.
Legal basis
- § 390 SGB V§ 390 SGB V IT-Sicherheit in der vertragsärztlichen und vertragszahnärztlichen Versorgung(1) Die Kassenärztlichen Bundesvereinigungen legen in einer Richtlinie die Anforderungen zur Gewährleistung der IT-Sicherheit in der vertragsärztlichen und vertragszahnärztlichen Versorgung fest. (2) Die Richtlinie nach Absatz 1 umfasst insbesondere auch - 1. Anforderungen an die sichere Installation und Wartung von Komponenten und Diensten der Telematikinfrastruktur, die in der vertragsärztlichen und …Open original (gesetze-im-internet.de) ↗Duty of the KBV and KZBV to set the requirements; binding for practices (para. 6); certified service providers (para. 7)
- § 391 SGB V§ 391 SGB V IT-Sicherheit in Krankenhäusern(1) Krankenhäuser sind verpflichtet, nach dem Stand der Technik angemessene organisatorische und technische Vorkehrungen zur Vermeidung von Störungen der Verfügbarkeit, Integrität und Vertraulichkeit ihrer informationstechnischen Systeme, Komponenten oder Prozesse zu treffen, die für die Funktionsfähigkeit des jeweiligen Krankenhauses und den Schutzbedarf der verarbeiteten Patienteninformationen maßgeblich sind. (2) …Open original (gesetze-im-internet.de) ↗Distinction from hospitals
- Part A IV of the guidelineA. IV. IT-Sicherheitsrichtlinie KBV Anforderungen zur Gewährleistung der IT-Sicherheit in Praxen1. Praxen nach A. III. 1. haben die Anforderungen aus Anlage 1 und 5 umzusetzen, soweit die Zielobjekte in der Praxis genutzt werden. 2. Praxen nach A. III. 2. haben die Anforderungen aus Anlage 1, 2 und 5 umzusetzen, soweit die Zielobjekte in der Praxis genutzt werden. 3. Praxen nach A. III. 3. haben die Anforderungen aus Anlage 1, 2, 3 und 5 umzusetzen, soweit die Zielobjekte in der Praxis genutzt werden. 4. …Open original (KBV – Richtlinie nach § 390 SGB V, Fassung vom 31.03.2025 (PDF)) ↗Target objects and applicability
- Annexes 1 to 5 of the guidelineAnlage 1 Nr. 1 IT-Sicherheitsrichtlinie KBV Geregelte Einarbeitung neuer MitarbeitenderMitarbeitende müssen zu Beginn ihrer Beschäftigung in ihre neuen Aufgaben eingearbeitet werden. Die Mitarbeitenden müssen über bestehende Regelungen, Handlungsanweisungen und Verfahrensweisen informiert werden.Open original (KBV – Richtlinie nach § 390 SGB V, Fassung vom 31.03.2025 (PDF)) ↗Requirements by practice size, large medical equipment and telematics infrastructure
Key dates
- KBV guideline in force in the version of 31.03.2025 · Part B no. 1 (KBV)B. IT-Sicherheitsrichtlinie KBV Inkrafttreten und Geltung1. Diese Richtlinie tritt am Tag nach der Veröffentlichung in Kraft. Sie ersetzt die bisherige Richtlinie nach § 75b SGB V über die Anforderungen zur Gewährleistung der IT-Sicherheit vom 16.12.2020 und setzt diese außer Kraft. 2. Diese Richtlinie gilt ab dem Tag nach ihrer Veröffentlichung. Hiervon ausgenommen sind folgende mit dieser Richtlinie neu hinzugekommenen Anforderungen: - A1) 1-7 Personal - A1) 8-10 …Open original (KBV – Richtlinie nach § 390 SGB V, Fassung vom 31.03.2025 (PDF)) ↗
- KZBV guideline version 1.1 in force · Part B (KZBV)B. IT-Sicherheitsrichtlinie KZBV Inkrafttreten und GeltungDiese Richtlinie ersetzt die bisher geltende Richtlinie nach § 75b SGB V vom 01.02.2021, veröffentlicht in Ausgabe Nr. 3/2021 der zm, und tritt vorbehaltlich des Satzes 2 am Tag nach ihrer Veröffentlichung in den zm in Kraft. Die folgenden mit dieser Richtlinie neu hinzugekommenen oder inhaltlich geänderten Anforderungen treten am 02.01.2026 in Kraft. Neue Anforderungen: - A1) 1-7 Personal - A1) 8-10 …Open original (KZBV – Richtlinie nach § 390 SGB V, Version 1.1 vom 01.07.2025) ↗
- New requirements of the KBV guideline apply · Part B no. 2 (KBV)B. IT-Sicherheitsrichtlinie KBV Inkrafttreten und Geltung1. Diese Richtlinie tritt am Tag nach der Veröffentlichung in Kraft. Sie ersetzt die bisherige Richtlinie nach § 75b SGB V über die Anforderungen zur Gewährleistung der IT-Sicherheit vom 16.12.2020 und setzt diese außer Kraft. 2. Diese Richtlinie gilt ab dem Tag nach ihrer Veröffentlichung. Hiervon ausgenommen sind folgende mit dieser Richtlinie neu hinzugekommenen Anforderungen: - A1) 1-7 Personal - A1) 8-10 …Open original (KBV – Richtlinie nach § 390 SGB V, Fassung vom 31.03.2025 (PDF)) ↗
- New and amended requirements of the KZBV guideline apply · Part B (KZBV)B. IT-Sicherheitsrichtlinie KZBV Inkrafttreten und GeltungDiese Richtlinie ersetzt die bisher geltende Richtlinie nach § 75b SGB V vom 01.02.2021, veröffentlicht in Ausgabe Nr. 3/2021 der zm, und tritt vorbehaltlich des Satzes 2 am Tag nach ihrer Veröffentlichung in den zm in Kraft. Die folgenden mit dieser Richtlinie neu hinzugekommenen oder inhaltlich geänderten Anforderungen treten am 02.01.2026 in Kraft. Neue Anforderungen: - A1) 1-7 Personal - A1) 8-10 …Open original (KZBV – Richtlinie nach § 390 SGB V, Version 1.1 vom 01.07.2025) ↗
The transitional periods have expired; all requirements apply today. The guideline requires no certificate and no notification to an authority, but implementation must be demonstrable at any time.
How Complass helps
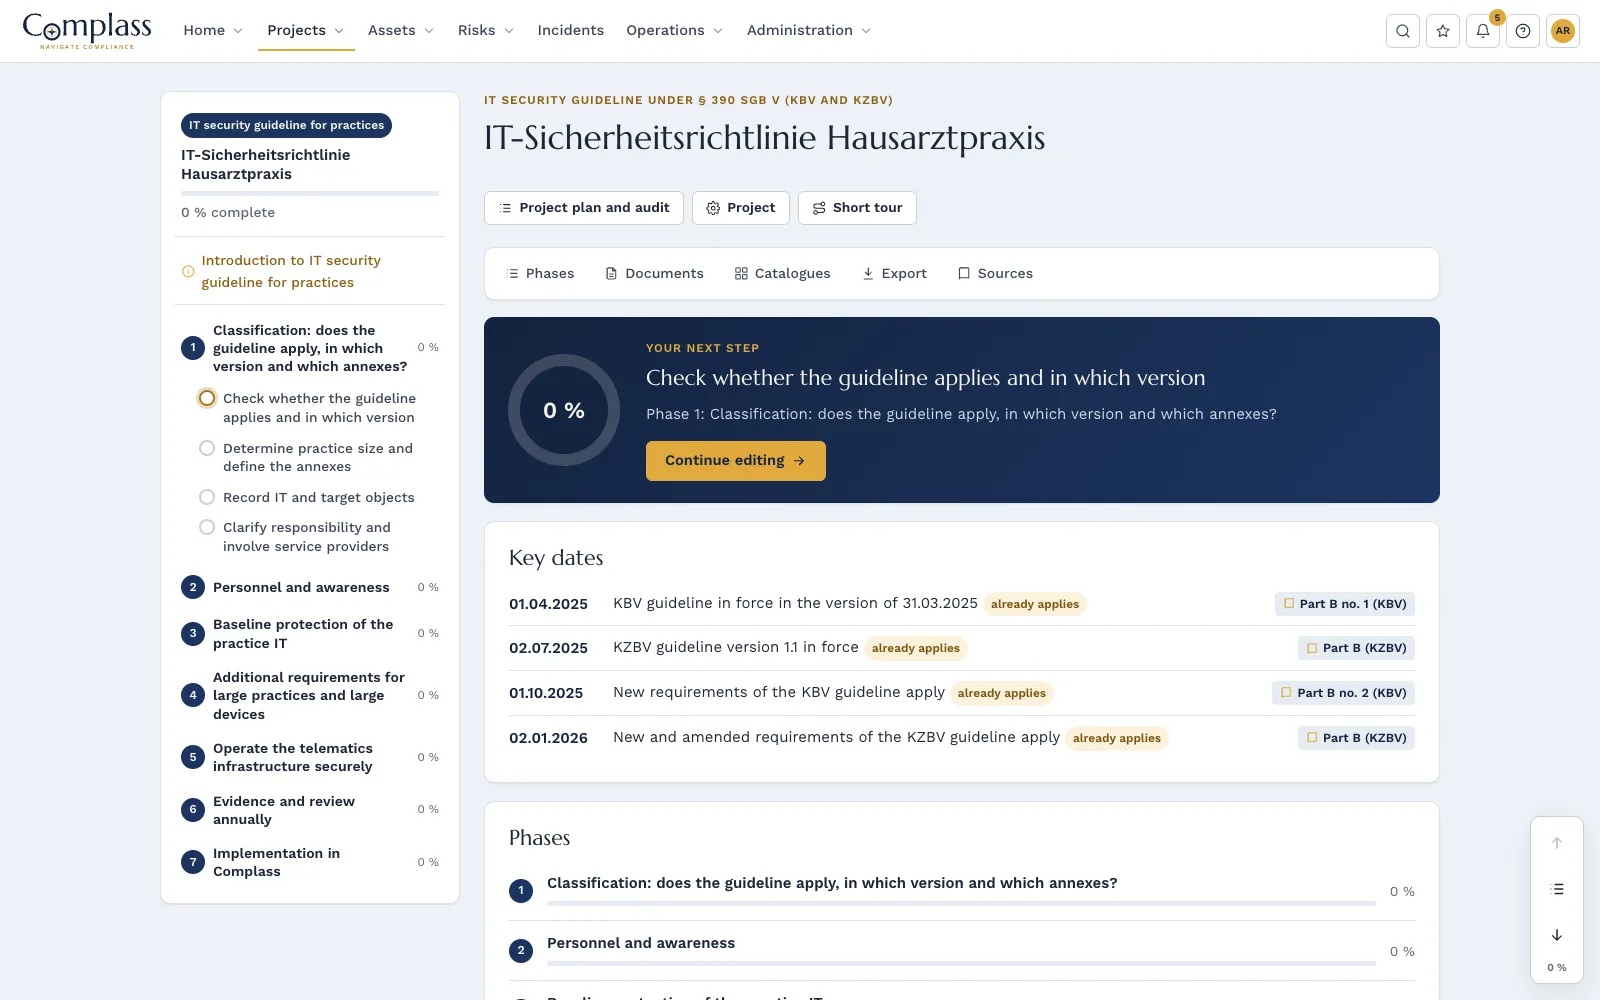
- 7phases
- 20guided steps
- 13document templates
- 92requirements in the catalogue
Seven phases up to the annual review
Classification with version and annexes, staff and awareness, baseline protection of the practice IT, additional requirements for large practices and large medical equipment, telematics infrastructure, evidence and annual review.
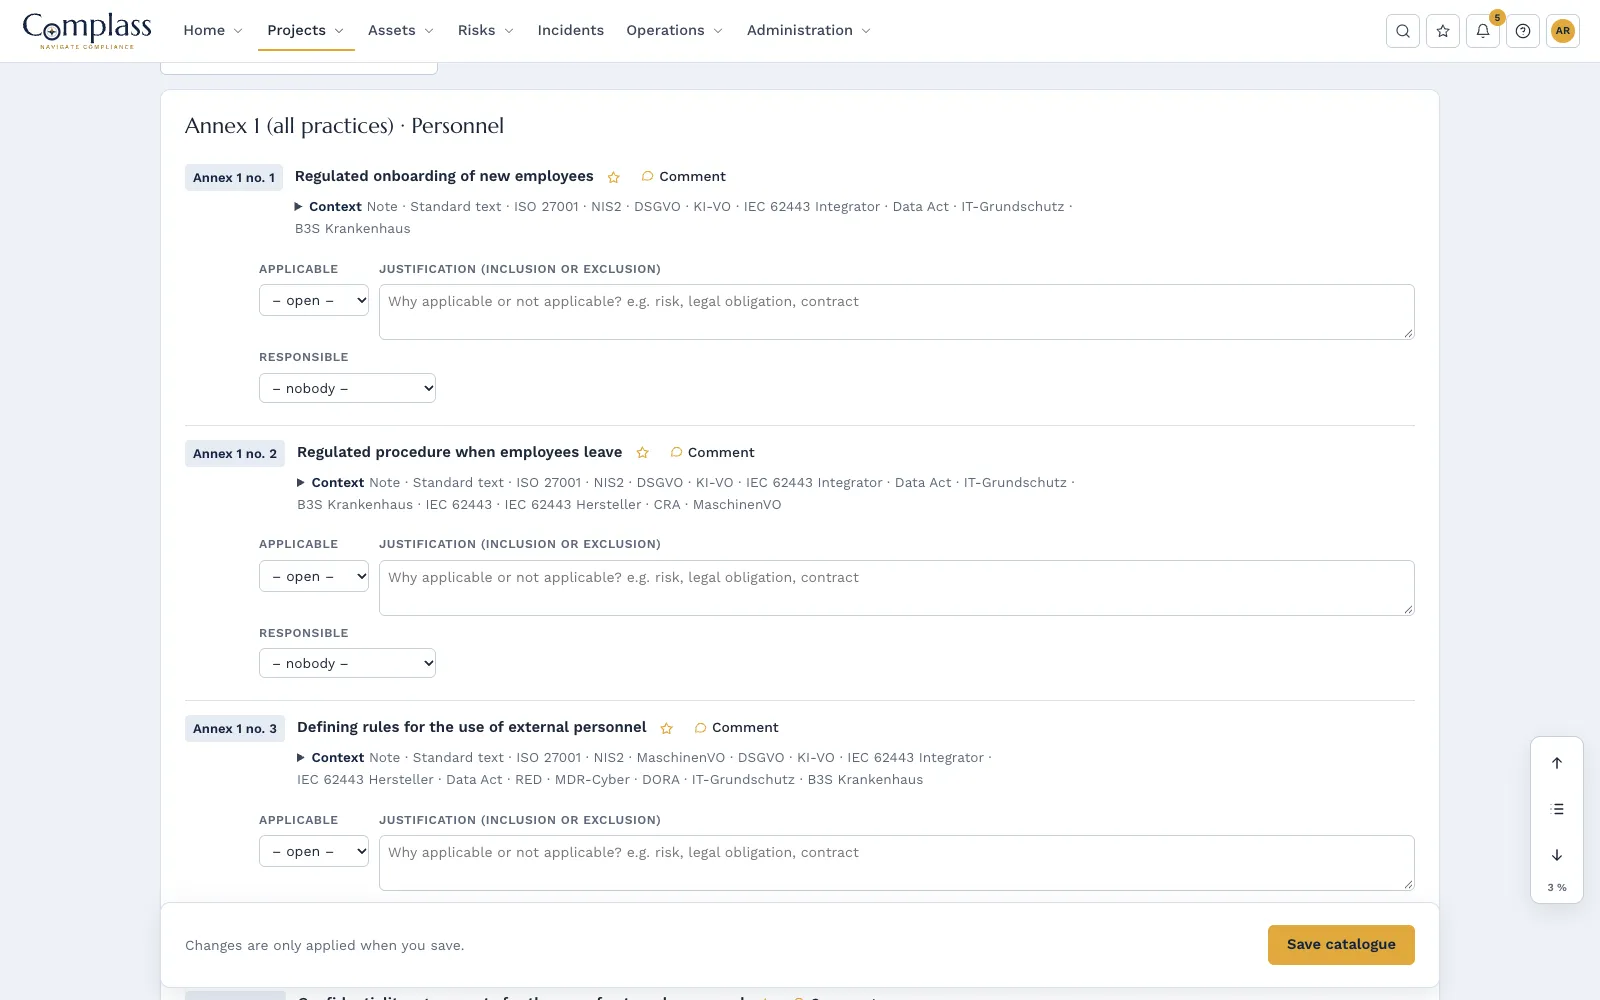
All 92 requirements in their original wording
KBV and KZBV versions side by side, with implementation hints, status and evidence per requirement. You exclude annexes and target objects that do not apply, with a reason.
Templates
Including practice profile, register of IT and target objects, network plan, backup concept, access and authorisation concept, policy for mobile devices, operation of the telematics infrastructure and annual review.
Training for the practice team
Course on the IT security guideline with seven units for practice owners and medical and dental assistants, with evidence of participation and learning success. Plus an IT register, business continuity management for an outage of the practice management system, the telematics infrastructure or the internet, and incident recording.
The phases in the module
- Classification: does the guideline apply, in which version and which annexes?
- Personnel and awareness
- Baseline protection of the practice IT
- Additional requirements for large practices and large devices
- Operate the telematics infrastructure securely
- Evidence and review annually
- Implementation in Complass
Catalogue: Requirements of the IT security guideline (Annexes 1 to 5)
Matching modules
Asset management
IT and OT assets in one place, agentless capture, with SBOM, vendor advisories, end of support, licence reconciliation, identities, relationships and zones per IEC 62443-3-2.
Learn moreIncident management
Record incidents, check reporting obligations under NIS2, the CRA and the GDPR and track the reporting deadlines with a countdown.
Learn moreCompliance management
Implement frameworks with guidance: phases, templates, document pyramid, catalogues, gap analysis, objectives and action plan up to the audit in the auditor portal.
Learn moreFrequently asked questions
Our IT service provider takes care of everything. Do we still need this?
The service provider can implement the technology, but responsibility stays with the practice management. Rules for the team, training and evidence are up to you. In Complass you record which requirements the service provider confirms and which the practice implements itself.
We are a dental practice. Does the KBV version apply to us?
No, dental practices implement the KZBV guideline. Both versions have the same structure and numbering; for every requirement Complass shows the KBV wording and, where it differs, the KZBV wording.
Do we need a certificate?
No. The guideline does not require a certificate. You must, however, be able to demonstrate implementation, for example to the regional association of statutory health insurance physicians or dentists, the data protection authority or, after an incident, to insurers.
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.